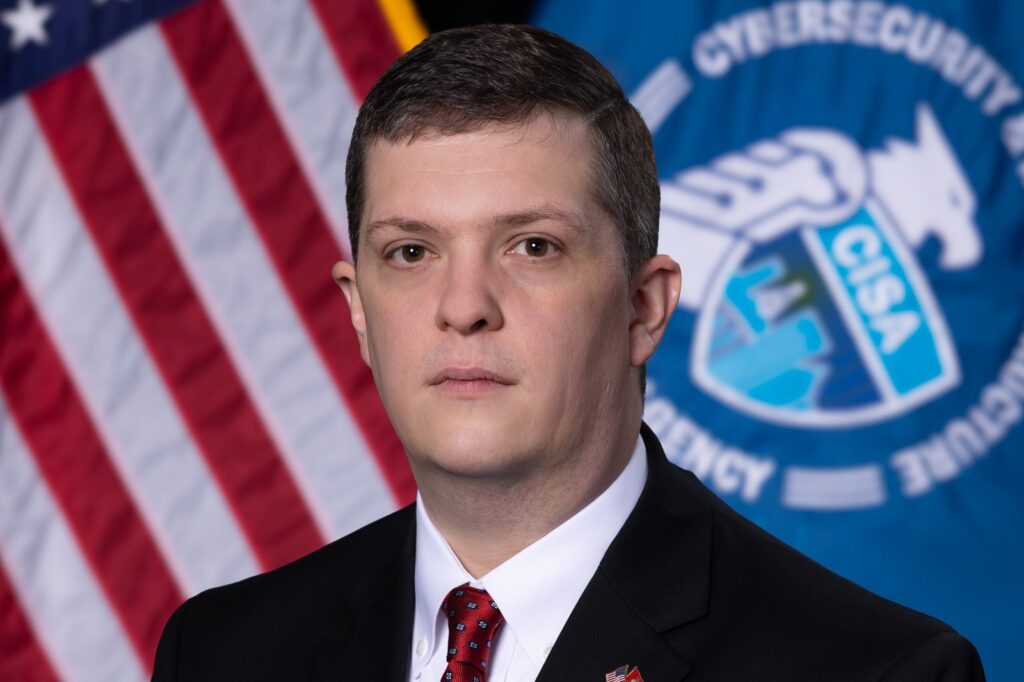
WASHINGTON, DC, November 18, 2026 — The Cybersecurity and Infrastructure Security Agency has zeroed in on roughly 100 companies that own critical infrastructure for priority security hardening talks, while a bipartisan bill introduced today aims to give the agency fast-track hiring authority for artificial intelligence talent. Acting Director Nick Andersen disclosed the target list Tuesday, and Reps. Josh Gottheimer and Vince Fong unveiled the BRIDGE AI Act on Wednesday as Iranian-linked attacks on food refrigeration systems escalate in Europe.
The shift is a focused engagement list built on adversary intelligence
CISA did not pick the 100 companies at random. The agency ran an intergovernmental Homeland Defense Working Group to identify firms providing functions vital to the economy, public health, national security and defense critical infrastructure. Then it overlaid five to six years of intelligence on where adversaries were pre-positioning and directing their research and development budgets. Companies appearing on both lists became targets for initial engagement, Andersen said after speaking at FedTalks. The conversations will vary widely and include sector risk management agencies, IT and operational technology providers, and cybersecurity vendors. The goal is to advance CISA’s 2030 strategy centered on resilience and minimum viability.
What’s changing: a legislative push for AI hiring speed
The BRIDGE AI Act, introduced November 18, would give CISA a fast way to bring in private-sector AI and emerging technology specialists to hunt intruders, patch vulnerabilities and stress-test AI tools before they are exploited. Gottheimer said adversaries are using AI to attack networks faster than ever and CISA lacks the in-house expertise to keep pace. Fong pointed to cyberattacks on schools, hospitals and water systems in California’s Central Valley. The release cited recent software outages affecting classified systems and this summer’s attacks on municipal water systems in at least a dozen states as evidence of the gap.
Iranian-linked refrigeration attacks heighten urgency
The legislation arrived the same week CISA, the FBI and the departments of Health and Human Services, Agriculture and Transportation warned food retailers and cold-chain operators about Iranian-linked intrusions. Hackers raised temperatures to 120°F at hundreds of French supermarkets on October 11 and 12, spoiling millions of euros in food. French Foreign Minister Jean-Noel Barrot attributed the operation to Iran’s Islamic Revolutionary Guard Corps on November 9. A second wave hit more than 100 grocery retailers across seven European countries November 2 and 3 using the same method. CISA Acting Executive Assistant Director for Cybersecurity Chris Butera said every organization depending on refrigeration and monitoring systems should assume it could be a target. More than half a dozen U.S. military commissaries experienced outages in late August at bases in California, New Mexico, Rhode Island, Arkansas, Wyoming, Georgia and Arizona.
Budget refocus and a funding cut for state and local support
The White House has requested $2.49 billion for CISA in fiscal 2027, refocusing the agency on its core cyber mission and critical infrastructure safeguarding. The proposal acknowledges a more constrained financial environment. In March 2025, CISA cut $10 million — about half the budget — for the Multi-State Information Sharing and Analysis Center, ending the cooperative agreement by September 2025. MS-ISAC previously served over 18,500 government entities for free and has since moved to a membership model to replace the lost funding. The Department of Homeland Security still designates MS-ISAC as a key cybersecurity resource for state, local, tribal and territorial governments.
From NPPD to the front line of digital resilience
CISA originated as the National Protection and Programs Directorate in 2007 and was elevated to a federal agency by the Cybersecurity and Infrastructure Security Agency Act of 2018. The law expanded its footprint to include election security, 5G network security, census protection and the U.S. response to the COVID-19 pandemic. Today it coordinates cybersecurity across all federal levels and with U.S. states against private and nation-state hackers. The agency’s threat hunting unit, with more than 700 professionals, played key roles in the response to the Salt Typhoon infiltration of U.S. telecommunications networks and the SolarWinds malware attack linked to Russia’s Foreign Intelligence Service.
Sources
- Cybersecurity and Infrastructure Security Agency
- How CISA is prioritizing companies for talks about security improvements
- RELEASE: On the Heels of Weekend Attacks, Gottheimer, Fong Announce Bipartisan Legislation to Strengthen Government Cyber Defenses
- It’s time to get serious about cyber security
- CISA's Thompson to Keynote 2026 Homeland Security Summit
- Cybersecurity group retools after funding cut
Photo: Unknown authorUnknown author (Public domain)