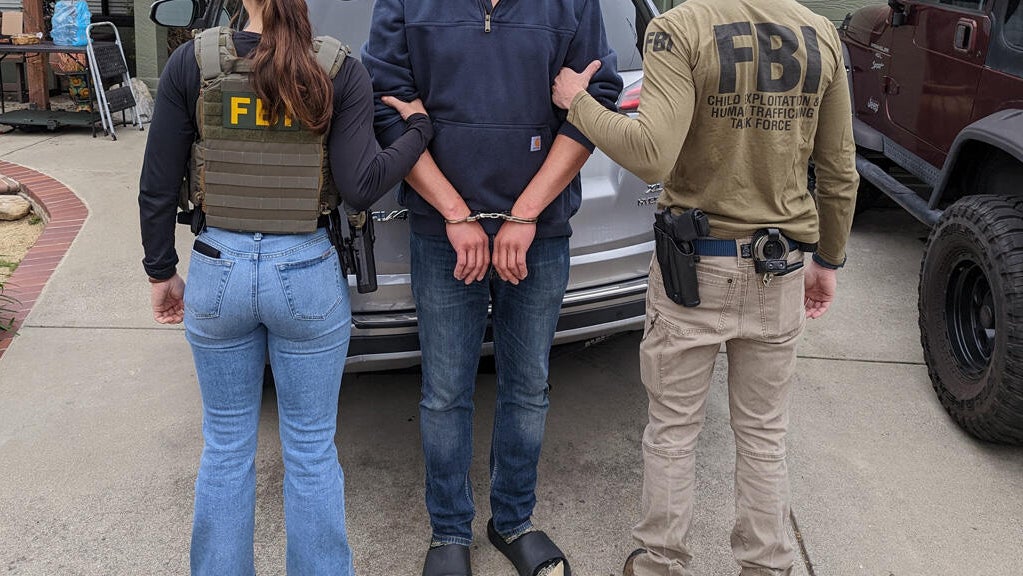
Philadelphia, October 13 — Edward Dubrovsky, a 54-year-old Canadian cybersecurity executive, was arrested by the FBI in Pennsylvania on Thursday while attending a cybersecurity conference in the Philadelphia area. The arrest is part of an ongoing investigation into the ransomware gang ShinyHunters. Court documents released by multiple media outlets confirm the detention but do not yet show a public FBI statement linking Dubrovsky directly to the group.
The indictment charges him with ‘conspiracy to threaten to impair the confidentiality of information with the intent to extort money’ and ‘interference with commerce by threats,’ both tied to alleged extortion activities. Dubrovsky has not entered a plea.
Officially, Dubrovsky holds an executive position at a cybersecurity firm where his responsibilities include working with ransomware victims to negotiate payments with hackers for data decryption or deletion. This role places him at the intersection of incident response and threat actor engagement — a space where legal boundaries can blur, especially when negotiations involve entities like ShinyHunters, known for aggressive data-theft tactics. ShinyHunters has been linked to a series of high-profile breaches across healthcare and public sectors.
The group claimed responsibility for the July hack on DentaQuest, the second-largest dental insurance company in the United States, which affected approximately 15 million individuals. In August, they asserted involvement in a cyberattack on pharmaceutical distributor McKesson, claiming to have exfiltrated records on ‘tens of millions’ of patients and more than 284 million individual documents via a phishing campaign, as reported exclusively by CyberInsider.
Earlier in April, the gang took credit for a breach at Medtronic, the Irish-American medical device manufacturer, threatening to sell the stolen data on its dark web blog. Investigators believe ShinyHunters may have accessed FBI employee data through a compromise of a third-party vendor managing FBIJobs.gov, although the FBI has not publicly confirmed this connection. Over time, several individuals have been arrested in relation to the gang, but the core membership remains unidentified.
The FBI has not disclosed any names of suspects in this latest operation, maintaining secrecy around the scope of its crackdown. The case raises questions about the dual-use nature of cybersecurity expertise — particularly how skills meant to defend against ransomware can be repurposed or misdirected in the shadow economy of cyber extortion. As ransomware groups evolve their tactics, targeting supply chains and leveraging phishing at scale, the line between defence and facilitation comes under increasing scrutiny.
What happens next in the legal process will depend on Dubrovsky’s plea and any further evidence presented by prosecutors. For now, the arrest marks a rare public move against someone operating near the fault line of incident response and illicit negotiation — a development the cybersecurity community will watch closely.