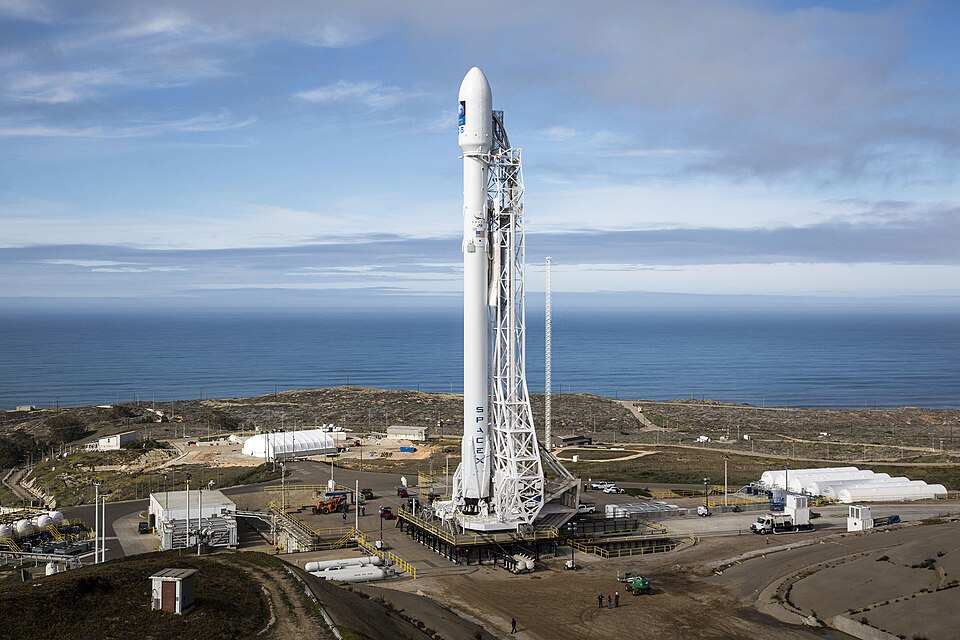
KYIV, July 25 — Two alleged agents arrested in Kyiv this month mark the first known domestic operation targeting the misuse of SpaceX’s Starlink satellite internet to aid Russian strikes. The case cuts to a festering problem: a technology hailed as a wartime lifeline has become a dual-use vulnerability. SpaceX, founded by Elon Musk in 2002, launched its first operational Starlink satellites in 2019.
After Russia’s full-scale invasion of Ukraine on February 24, 2022, the company activated service in the country with remarkable speed. By 2024, SpaceX had donated over 42,000 terminals.
Starlink became vital not only for civilian internet access amid Russian attacks on infrastructure but also for Ukrainian military communications and drone operations. The innovation was genuine — a satellite constellation that could be deployed and powered in the field, bypassing damaged ground networks. But the mechanics here carried a hidden risk.
Each terminal is small, portable, and can be activated through modified software. That same flexibility — the very feature that made Starlink so effective for Ukrainian forces — opened a back door.
The Dual-Use Dilemma
By early 2024, reports emerged that Russian forces were using stolen or illegally acquired Starlink terminals in occupied areas of Donetsk, Zaporizhzhia, and Kherson. SpaceX has officially prohibited the use of Starlink for military purposes by any party. On closer reading, that prohibition is a policy statement, not a technical barrier.
The catch is enforcement: with thousands of terminals in the field, distinguishing authorised from unauthorised users — especially behind enemy lines — is nearly impossible. The situation exposes a foundational tension in modern satellite communications.
A system designed for mass consumer access, with low-cost hardware and global coverage, inevitably becomes a dual-use technology. The same constellation that keeps a hospital online can also guide a drone. SpaceX’s stated policy is clear, but the architecture of Starlink resists fine-grained control.
The company can deactivate individual terminals — but only if it knows they are in the wrong hands.
The SBU Strikes
The SBU’s arrest of two alleged agents in Kyiv changes the calculus. It is the first known domestic operation specifically targeting Starlink misuse to aid Russian strikes. That means Ukrainian intelligence has moved from passive monitoring to active pursuit — not just of the terminals themselves, but of the people handling them inside Ukraine’s own territory.
The case raises immediate questions. How are stolen terminals reaching Russian lines?
Are they being smuggled from Ukrainian-controlled areas, or captured on the battlefield and then reactivated? What role did the alleged agents in Kyiv play in that supply chain? The SBU has not released details of the charges, but the operation signals a new front in the electronic warfare campaign: controlling access to a commercial satellite service that has become a strategic asset.
What Next?
The bigger question is what this means for global regulations on dual-use technology. Starlink exists in a regulatory vacuum — no single treaty governs how a private satellite constellation can be used in a war zone. SpaceX’s prohibition is voluntary and hard to verify.
The Ukrainian experience will almost certainly shape future rules, but that process is slow. For now, the company, the military, and the intelligence services are improvising.
The arrest in Kyiv is a step toward tightening that control. But as long as terminals remain in the field — and the software remains modifiable — the vulnerability will persist. Follow the hardware, and the human chain that moves it.
That is where the next breakthrough, or the next breach, will come.